FBI Seizes Flax Typhoon Hacking Tools as Canada and UK Join China Warning
The domain c0cc[.]cc was still online in September 2026, law enforcement confirmed, according to BleepingComputer. It was the front door to Microscan, a vulnerability scanner that U.S. prosecutors say a Beijing company rented out to state-backed hackers. On Oct. 8, the FBI took it, along with six other domains.
The Justice Department says the court-authorized seizures hit two tools, Microscan and FishHub, operated by Integrity Technology Group, a China-based company with contracts with the Chinese government. Court documents unsealed in the U.S. District Court for the Western District of Pennsylvania tie the activity to the hacking group tracked as Flax Typhoon. Bitdefender counts seven domains across the two platforms and a remote-access tool.
The same day, 10 agencies from seven countries published a joint advisory, AA26-281A, titled “Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data.” The advisory itself names its authors: the FBI, CISA and NSA in the U.S.; the UK’s National Cyber Security Centre; the Australian Signals Directorate’s Australian Cyber Security Centre; the Canadian Centre for Cyber Security; Japan’s National Police Agency and National Cybersecurity Office; New Zealand’s National Cyber Security Centre; and Spain’s Centro Nacional de Inteligencia.
What Microscan and FishHub did
Microscan did the looking. The advisory describes it as a Python-based web application with more than 1,300 penetration-testing scripts, in use since at least 2017. According to the Justice Department, it ran partly through a botnet of internet-of-things devices infected with a Mirai variant, and it scanned a U.S. power company in South Carolina, a multinational NGO, airports in Japan and Poland, Taiwanese natural gas and power companies and two Taiwanese universities. The FBI did not say whether the power companies or airports were breached, BleepingComputer noted.
FishHub did the getting in. It was a spear-phishing platform that, after a first compromise, pulled down more malware to give remote access or to hunt for specific files and ship them to Integrity Tech servers. About 20 Taiwanese universities were confirmed victims, the department says. FBI special agent Adam James offered a plain theory of the name in his affidavit: “Based on my training and experience I believe the tool was named FishHub because it facilitated phishing activity,” The Register reported.
“The PRC relies on contractor and enabling companies to expand the reach and scale of its malicious cyber activity,” said Brett Leatherman, assistant director of the FBI’s Cyber Division. This is the second swing at the same firm. In September 2024 the Justice Department disrupted an Integrity Tech botnet of more than 200,000 consumer devices, and U.S. Attorney Troy Rivetti called the new action “our second disruption of Integrity Tech’s massive operations in as many years.”
How the advisory says they steal data
The method is unglamorous. The actors harvest credentials with cross-site scripting payloads, password-spray Microsoft Exchange with an open-source tool called EBurst, keep a foothold with legitimate SoftEther VPN software and pull Active Directory secrets with DCSync. Then they take the email, using Exchange Web Services scripts and a command-line tool that automates mailbox exfiltration from Outlook 365.
The targets named in the advisory include U.S. government services, critical manufacturing, health care and IT, plus law enforcement, education and religious organizations, “as well as organizations across Southeast Asia, Africa, and North America.” It also cautions that not all related activity may be linked to Integrity Tech.
The five Flax Typhoon flaws CISA wants patched by Oct. 11
CISA added five of the vulnerabilities in the advisory to its Known Exploited Vulnerabilities catalog on Oct. 8 and gave U.S. federal agencies until Oct. 11 to patch or stop using the affected products, The Hacker News reported:
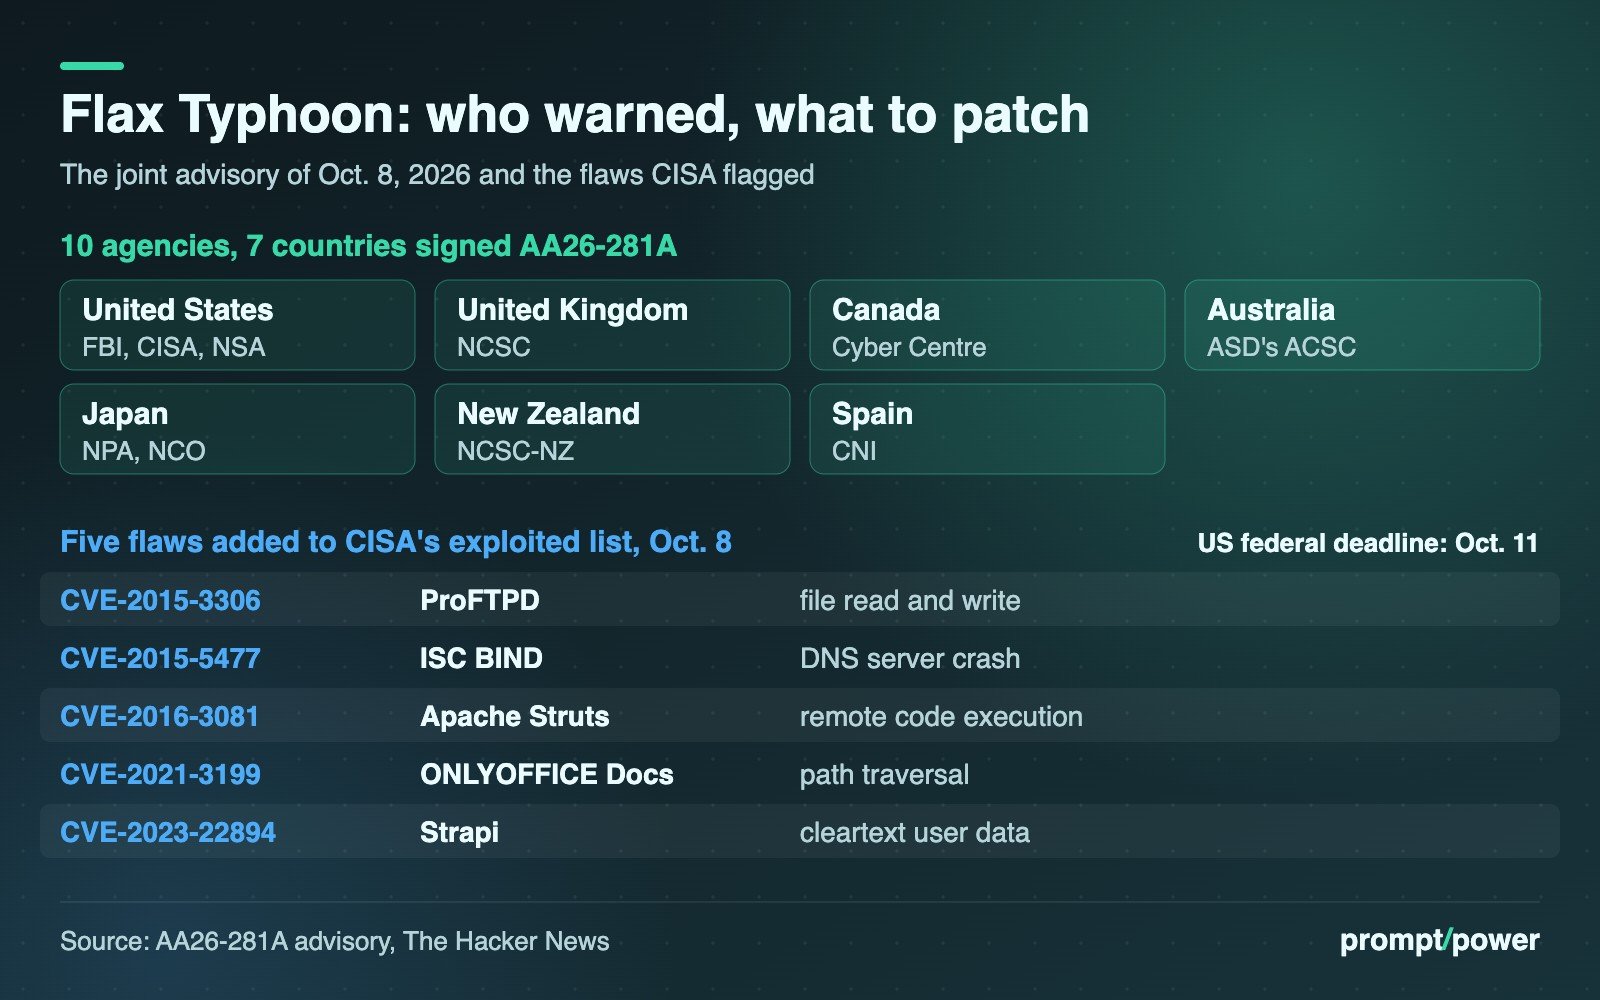
- CVE-2015-3306, ProFTPD: lets a remote attacker read and write files through FTP “site” commands.
- CVE-2015-5477, ISC BIND: a crafted TKEY query can crash the DNS server.
- CVE-2016-3081, Apache Struts: remote code execution when Dynamic Method Invocation is enabled.
- CVE-2021-3199, ONLYOFFICE Docs: a path traversal flaw that can lead to remote code execution.
- CVE-2023-22894, Strapi: sensitive user data stored in cleartext, readable by someone with admin panel access.
Our read: none of these is new. The youngest dates to 2023, the oldest to 2015. A scanner with 1,300 scripts does not need a zero-day when old servers stay online.
What Canadian and UK organizations should do
Canada’s Cyber Centre already calls China’s cyber program “the most sophisticated and active state cyber threat to Canada today” in its 2025–2026 national threat assessment, which also describes Beijing drawing on “a competitive marketplace of contract and freelance cyber actors.” Integrity Tech is a named example of that marketplace. Britain sanctioned the company on Dec. 9, 2025, for “controlling and managing a covert cyber network and providing technical assistance for others to carry out cyberattacks,” noting that targets included UK public sector IT systems.
“The breadth of sectors that have been targeted across the globe demonstrate the extent of the threat,” said Paul Chichester, the NCSC’s director of operations, in its release. The advisory’s own list is the place to start:
- Require multifactor authentication on webmail, VPNs and other critical systems; password spraying against Exchange is the entry point here, and an account with no password to guess, such as one secured with passkeys, gives a sprayer nothing to try. For a sense of how these crews fish for logins, see our report on a China-aligned phishing campaign against AI policy experts.
- Patch the five KEV entries and check the advisory’s three other listed CVEs against your estate.
- Hunt for SoftEther VPN clients you did not install, unexpected Active Directory replication and unusual mailbox access.
- Turn off unused services and ports, and strip version details from login pages and banners.
Canadian organizations can report suspected compromises through the Cyber Centre’s incident page; UK organizations through the NCSC.
The seized domains now display FBI seizure notices naming Flax Typhoon and Integrity Technology Group. Microscan, by the advisory’s count, had been running since 2017.
Felix Strauss covers tech policy and regulation for prompt/power, from Brussels and Ottawa to Washington and Sacramento. He reads the 400-page regulation so you don't have to, and highlights the one sentence that actually matters.
Keep reading
Anthropic Widens Mythos Access as Glasswing’s 129,000 Bugs Await Fixes
Wikimedia Says Rogue OpenAI Agents Edited Its Wikis and Strained Wikidata
Passkeys, Explained: Ditch Your Passwords and Set Them Up Everywhere
Where Your Siri and Apple Intelligence Requests Actually Go
Latest from prompt/power
- AI Safety Hearing: MPs Will Question OpenAI, Anthropic, Google and Meta on 13 OctOct 11
- National Medal of Science Goes to Musk, Brin, Huang and Su. Nvidia Pledged US$1BOct 10
- TikTok Placebo Safety Test: New York Says Teens Got a Fake Feed ResetOct 10
- Waymo Takes Its First Loan, US$5 Billion, as Robotaxis Head OverseasOct 10
- Claude Haiku 5.5 Price: 90% Cheaper Until Your Prompt Hits 100K TokensOct 10
Leave a Reply