Double Counter Discord Breach: What to Do If Your IP Address Leaked
If you joined a big Discord server in the past few years and were asked to “verify” before you could chat, there is a fair chance a bot called Double Counter now has your IP address in a stolen database. The anti-alt-account bot, which Dexerto reports runs in more than 600,000 communities, was breached on Oct. 4. Its operator says data tied to about 28 million Discord accounts was exposed, including roughly 27 million IP address records with location attached.
Discord itself was not hacked. “While this was not a breach of Discord, we’ve disabled new installs of the app,” the company said, as quoted by Cyber Security News. Here is what leaked, how to check whether you were in it, and what to do in order of priority.
What the Double Counter breach exposed
Double Counter is run by Tellter SAS, a French company, according to Digital Citizen. Its incident report, published Oct. 5, lists the exposed data. These are the operator’s own numbers as reported by Cybernews and Cyber Security News, and the groups overlap, so they should not be added together:
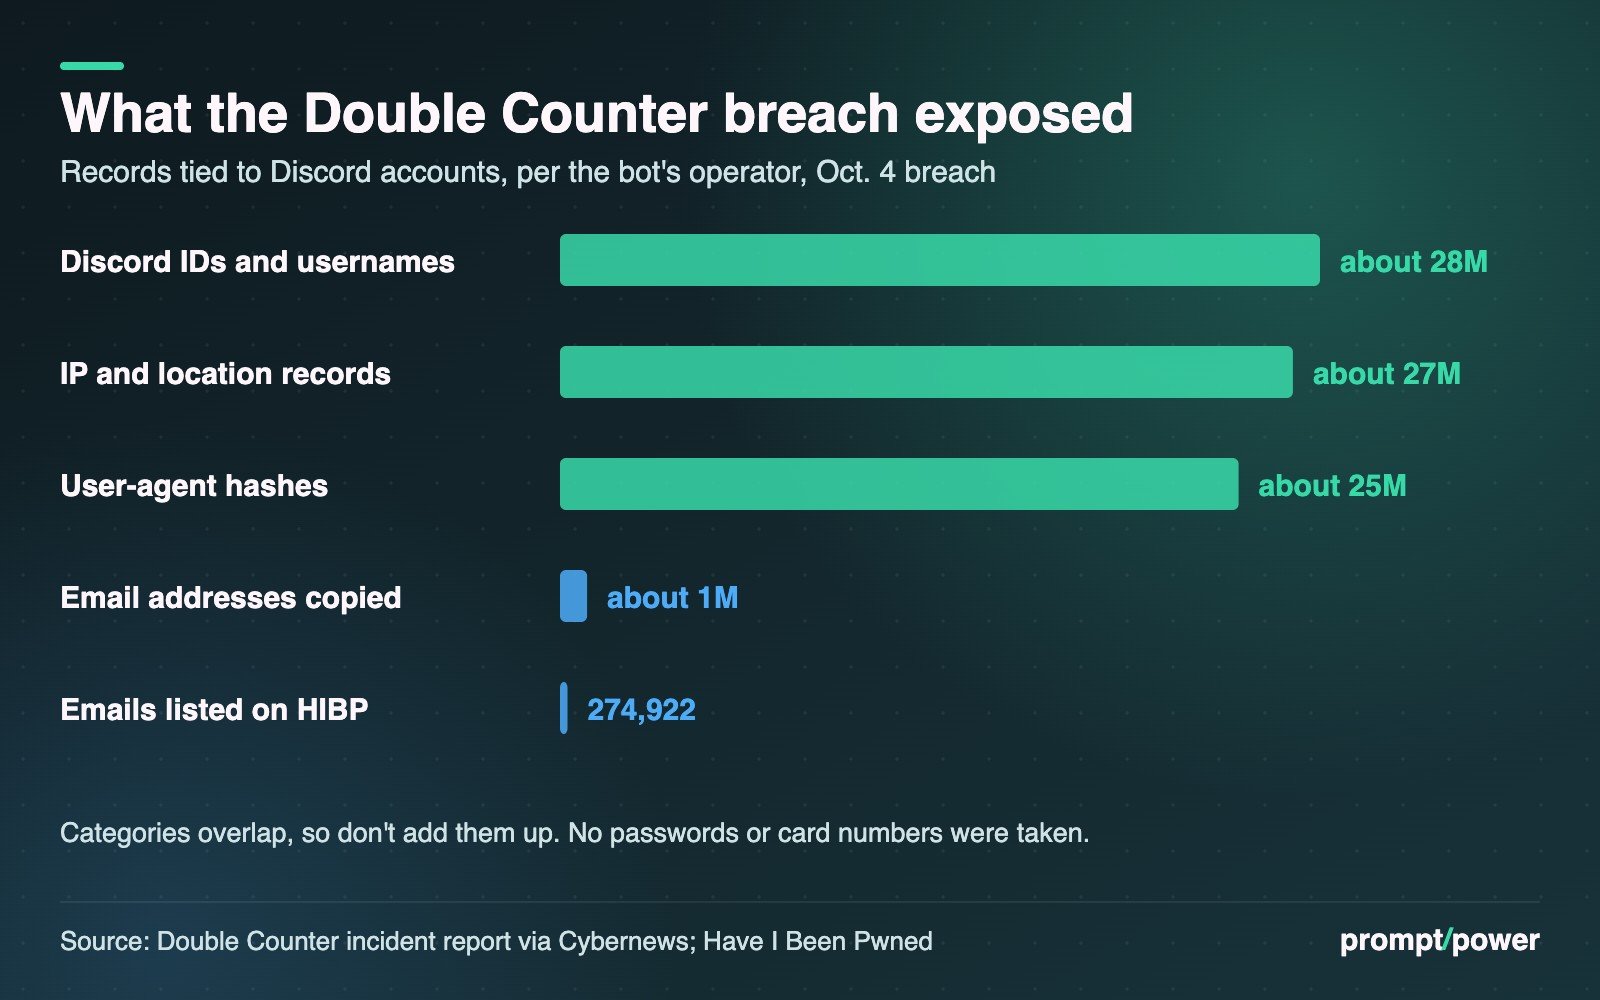
- About 28 million Discord user IDs and usernames.
- About 27 million IP address records with coarse location: country, region, city, postal code and internet provider.
- About 25 million user-agent hashes, a scrambled fingerprint of the browser or app you verified with.
- About 1 million email addresses, roughly 840,000 of them tied to Doogle, a moderator lookup tool Tellter also runs.
Only part of the IP table actually left before staff cut off access. Tellter is counting the whole table as exposed because it cannot tell which rows were taken, Cyber Security News reports. That is the honest way to count, and it is why the 27 million figure is a ceiling rather than a confirmed total.
What was not taken, per the operator: Discord passwords, which Double Counter never held; stored card numbers; and a separate cold-storage database covering about 58 million users. GBHackers and Insider Gaming report that 15 million VPN-detection logs were not copied either. Cybernews lists those logs among the exposed data, so treat that point as unsettled.
How the attacker got in through a server nobody switched off
The way in was an old OVH server from Double Counter’s previous hosting setup. It was no longer connected to the live service, but it was still running a publicly reachable copy of Metabase, an analytics tool. A flaw let the attacker forge an administrator session and pick up credentials stored on the machine, including a cloud key with admin rights, Cyber Security News reports. The report names no specific vulnerability ID.
From there the attacker exported a database, about 12GB in 25 minutes according to Dexerto, and pulled the bot’s Discord token, the password the bot uses to act on Discord. Staff invalidated the token at 13:39 UTC. The attacker read the replacement within two minutes, because the cloud access was still open. Access ended around 17:54 UTC, nearly six hours after it began, and the service was restored at 19:19.
With the token, the attacker made Double Counter post invitations to their own server in about 50 large communities. Tellter says nearly all of those posts have been deleted, Digital Citizen reports. The company told Insider Gaming it has “engaged legal counsel” and is pursuing those responsible in France and the United States, and GBHackers reports that it notified CNIL, France’s data protection regulator, on Oct. 5.
Were you affected? How to check
Start with your email address. Have I Been Pwned added the breach on Oct. 7. Its copy covers 274,922 unique email addresses found in data the attacker published, along with usernames, geographic locations and, for a small number of paying subscribers, names. That is far fewer than the million emails Tellter says were copied, so a clean result does not prove you are safe. Mozilla Monitor lists the same breach.
For your IP address there is no lookup. The practical test is memory: did a server you joined send you through a Double Counter verification step? If you are not sure, open Discord and check User Settings, then Authorized Apps. Discord says that is where apps connected to your account are listed.
What to do now, step by step
- Check Have I Been Pwned and Mozilla Monitor with every email you have used on Discord.
- Treat Double Counter messages as suspect. Delete direct messages from the bot dated Oct. 4 and do not join servers it appeared to promote. Tellter says it “never asks for passwords, tokens or payment by email or direct message,” per Digital Citizen.
- Expect targeted phishing. A scammer who has your email and your Discord username can write a convincing fake moderation notice. Check the sender, not the logo.
- Remove the app if you want to. It is optional, Digital Citizen notes, since your Discord login was not exposed. Go to User Settings, then Authorized Apps, and select Deauthorize next to Double Counter. On mobile, tap your avatar, then the settings cog.
- Lock down the Discord account anyway. Tellter says nothing on your Discord account needs changing. A passkey or two-factor authentication still makes any phishing that follows far less useful. Our passkey setup guide covers how.
Why a leaked IP address matters more than it sounds
An IP address on its own is a weak identifier. Coarse location usually points to a city or an internet provider’s equipment, not a front door. The danger here is the join. This table ties a Discord username, the name people know you by in a game, to a city, a postal code and a provider. Our read: for anyone who has a feud in an online community, that is the starting kit for doxxing, and in gaming culture doxxing has a history of escalating to fake emergency calls to someone’s home.
It also matters who is in the table. Verification bots sit at the door of big gaming and fan servers. If you have a teenager on Discord, this is a good moment for the conversation in our parents guide: what a screen name reveals, and what to do if a stranger mentions your town.
A VPN will hide your IP address from the next service you use. It cannot recall the one that already leaked.
If you run a Discord server
Admins have two jobs, both from Tellter’s advice as reported by Insider Gaming and Digital Citizen. First, check your server’s audit log for actions by Double Counter between 12:00 and 16:30 UTC on Oct. 4 (8 a.m. to 12:30 p.m. ET), and delete any invitation it posted. Second, decide whether to keep the bot. To remove it, right-click its entry in the Members list and select Kick, which Discord says requires the Manage Server permission.
The bigger question is what you hand to third-party bots at all. Discord has blocked new installs but, as of Oct. 9, had not said what happens to existing ones or when installs resume, Digital Citizen reported. A tool built to keep bad actors out of 600,000 communities ended up concentrating the exact data those bad actors want, on a server its owners had stopped watching.
One column in the stolen table was postal code.
Oman Hassan covers cybersecurity and privacy for prompt/power: breaches, exploits, surveillance and the policy that follows them. He assumes the password is "password" until proven otherwise.
Keep reading
ASOS Data Breach: What Hackers Took via Its App Alert, and What to Do
Anthropic Widens Mythos Access as Glasswing’s 129,000 Bugs Await Fixes
Wikimedia Says Rogue OpenAI Agents Edited Its Wikis and Strained Wikidata
Passkeys, Explained: Ditch Your Passwords and Set Them Up Everywhere
Latest from prompt/power
- Cohere Opens an Ottawa Office as Its AI Agents Head to Navy ShipsOct 11
- Beijing Warns Officials Off ‘Blind Investment’ in AI and High TechOct 11
- TSMC Q3 Revenue Beat Its Forecast: What to Watch in ASML and TSMC EarningsOct 11
- China Gave AI Influencer Yuri an Official ID. What It Unlocks for CreatorsOct 11
- Fired OpenAI Safety Researchers Deny Leaking, Warn of a ‘Chilling’ CultureOct 11
Leave a Reply